See how any app really works: reverse-engineer it with an AI agent — hands-on with REA
You’ve seen a feature in an app — a search box that reads your mind, a sync that never conflicts, an animation with impossible physics — and wondered how they built it. The source is closed and the docs say nothing. REA (morluto/rea, MIT) flips the power balance: one MCP server that wires your coding agent to the tools professional reverse engineers use — Ghidra, Hopper, JADX, packet captures — and lets you ask plain questions like “understand how search works in the Notes app, show me the evidence, and build a similar feature for my project.” The agent inspects the target, traces the relevant code, and answers with evidence attached. REA is the #1 trending repository on GitHub today, with 41,000+ stars. This walkthrough takes it from a fresh install to your first investigation.
- MIT licensed; morluto/rea; #1 trending repository on GitHub with 41,000+ stars; npm package rea-agents at version 6.2.0
- Setup: npx rea-agents setup shows a multi-select of supported agents (Claude Code, Codex, Cursor, Gemini CLI, VS Code, OpenCode, GitHub Copilot CLI, Windsurf, Devin, Antigravity, Grok Build, Claude Desktop), proposes config changes with backups, and waits for approval before writing anything; about 30 minutes total
- CLI: rea analyze, function, decompile, xrefs for native binaries via Ghidra/Hopper/IDA; static JavaScript and .NET inspection need Node alone — 'rea inspect-artifact ./app.asar --json' reads without running the application
- Showcase: a DX-Ball sound-pan calculation reconstructed into C passing 3,205 original-x86 test cases and reproducing all 63 compiled function bytes; Notion's Electron clipboard bridge traced; a DOS bullet-ring calculation recovered from 16-bit PC-98 instructions
- Caveats: static analysis reads files without executing (safe); runtime capture runs code under your permissions (read the runtime guide first); your agent's cloud sees every tool result; lawful research only — get authorization first
What you’ll need
- Node.js 22.19 or later (24.x or 26+ also fine) and npm.
- A coding agent that supports local MCP servers — Claude Code, Codex, Cursor, Gemini CLI, VS Code, OpenCode, GitHub Copilot CLI, Windsurf, Devin, Antigravity, Grok Build, or Claude Desktop. The full list is in the project’s installation guide.
- A target you are allowed to inspect: an extracted Electron app, a small binary you compiled yourself, or a website.
- (Optional) An existing Hopper, Ghidra, or IDA installation — needed only for deep native analysis. Static JavaScript and .NET inspection need no engine at all.
- About 30 minutes.
Step 1 — register REA with your agent
npx rea-agents setupSetup shows a multi-select of supported agents, proposes the exact configuration changes — registering REA’s MCP server plus matching workflow instructions, with backups of your existing config — and waits for your approval before writing anything. Restart the agent afterward. Two knobs worth knowing: rea setup --dry-run previews the plan without applying it, and --skill=false skips installing the workflow instructions if you only want the MCP server. Hopper installation is a separate question with its own explicit approval; the setup can also record verified paths for an existing Ghidra. The npm package is currently at version 6.2.0 and moves fast — rea update keeps it current, and the update prints the setup command to refresh your agent registrations.
Step 2 — ask your agent a real question
Understand how search works in the Notes app, show me the evidence,
and build a similar feature for my project.
That is the project’s own example prompt, and it captures the whole pitch: the agent calls REA through MCP, inspects the target without its source code, traces the relevant code, and comes back with findings plus the evidence and limitations behind each conclusion. Your agent then uses those findings to explain the behavior, or to write and test a version for your project. You are not operating the decompiler yourself — you are asking questions, and the answers arrive with receipts. The project’s showcase page has three worked cases that show the ceiling: a DX-Ball sound-pan calculation reconstructed into C that passes 3,205 original-x86 test cases and reproduces all 63 compiled function bytes, Notion’s Electron clipboard bridge traced from renderer through preload and IPC into the main process, and a DOS bullet-ring calculation recovered from the original PC-98 game’s 16-bit instructions.
Step 3 — inspect an Electron or JavaScript app from the terminal
You don’t need an agent for a direct inspection — the CLI runs the same workflows. Point it at an extracted application directory or an ASAR archive:
npx -y rea-agents@latest analyze-javascript-application /absolute/path/to/app --jsonThe result includes modules, imports, Electron boundaries, and the evidence. Static analysis reads the supplied files without running the application — safe against targets you don’t fully trust. For regular use, install the command once:
npm install --global rea-agents
rea --help
A generic rea analyze PATH selects the JavaScript workflow automatically for directories and .asar files. Output defaults to the project’s compact TOON format; pass --json when a script consumes it. To keep a structured record of an inspection:
set -o pipefail
rea inspect-artifact ./app.asar --json | jq . > inspection.json
Step 4 — go native with Ghidra or Hopper
For a native binary, configure an analysis engine first, then query it directly:
rea providers --json
rea analyze /absolute/path/to/program --provider ghidra --json
rea search /absolute/path/to/program "search" --provider ghidra --json
rea function /absolute/path/to/program main --provider ghidra --json
rea decompile /absolute/path/to/program 0x1000 --provider ghidra --json
rea xrefs /absolute/path/to/program 0x1000 --provider ghidra --json
function returns a function dossier, decompile returns pseudocode, xrefs maps cross-references. Substitute your target, search text, function name, or address. rea providers and rea capabilities list what each engine supports; set REA_ANALYSIS_PROVIDER as a standing preference, and diagnose a sick engine with rea doctor --provider ghidra --json. If a binary is large, the docs suggest raising Ghidra’s startup deadline with REA_GHIDRA_STARTUP_TIMEOUT_MS. REA starts Hopper when an operation needs it — on macOS a first-run dialog may ask you to choose demo mode or activate your license.
Step 5 — save snapshots and keep the evidence
Each CLI invocation is a separate process, so save results you will reuse. A snapshot retains successful analysis results for later queries, and REA reuses an exact result when the target bytes, operation, parameters, provider, and settings all match:
rea analyze /absolute/path/to/program --provider ghidra --snapshot /absolute/path/to/analysis/program.json
# Repeat the same query to reuse its saved result.
Snapshot files are local with owner-only permissions. Evidence bundles can be validated, exported to canonical form, and compared — useful when you want to diff two versions of the same app:
rea evidence-export /absolute/path/to/evidence/bundle.json /absolute/path/to/evidence/canonical.json
rea compare /absolute/path/to/evidence/left.json /absolute/path/to/evidence/right.json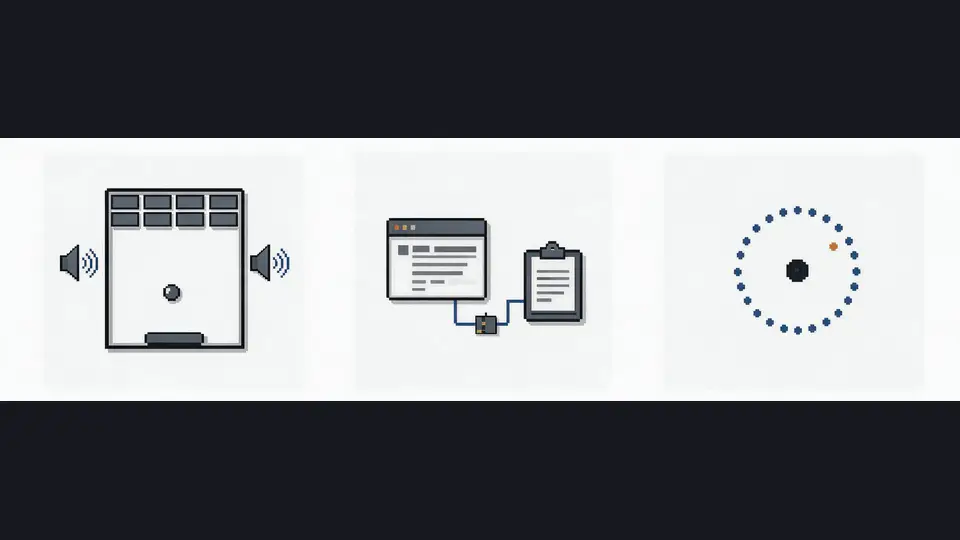
What you built
An agent that can investigate any app you point it at — native binaries, JavaScript and Electron apps, websites, .NET assemblies, Android APKs, firmware, even EVM bytecode and saved network captures — and explain how a feature works with evidence attached, then reimplement it for your project. Plus a terminal workflow for direct analysis: rea analyze for the overview, function/decompile/xrefs for the details, snapshots and evidence bundles for repeatable, diffable investigations. The loop is the same whether you drive it through chat or through bash: point at a target, get evidence-backed findings, ask for the reimplementation.
Honest limitations
- Deep native analysis needs an engine. Static JavaScript and .NET inspection work with Node alone, but pseudocode and disassembly require Hopper, Ghidra, or IDA — Ghidra is free, the others are commercial, and setup installs them only with your explicit approval.
- Static is safe; runtime is not free. Static analysis reads files without executing them. Runtime capture runs or interacts with the target under your user permissions — read the runtime guide for your target before launching anything you don’t trust.
- Local analysis, but your agent’s cloud sees the results. REA doesn’t upload your app anywhere; still, your agent receives every tool result, and its model provider has its own data policy. Keep genuinely sensitive targets away from hosted agents.
- Exit codes lie politely. Status 0 means the operation completed — but the result may still carry partial evidence, warnings, or unresolved questions. Read the output, not just the exit code.
- Lawful research only. The project ships this disclaimer itself: you are responsible for obtaining any required authorization and complying with applicable law. Keep it to your own apps, open-source targets, CTF practice binaries, and anything you have explicit permission to inspect.
Still: reverse engineering used to mean learning a disassembler before you could ask a single question. REA moves the bottleneck from tooling to curiosity — the hard part is no longer operating Ghidra, it’s knowing what to ask.